The CLOUD Act in three minutes
An American law that decides who can get at your data, even when it sits in Europe. Sounds complicated. It really isn’t.
You may never have heard of it, but the CLOUD Act can matter to European organisations that use American cloud services. Here’s the explanation, in three minutes.
What is it?
The CLOUD Act is an American law from 2018. It allows US law enforcement agencies to request data from American tech companies.
What’s the problem?
The location of the data centre doesn’t rule out such a request. Even when an American company processes data in Amsterdam, it can, under certain conditions, be obliged to hand it over.
That doesn’t mean all data is simply up for grabs. There are procedures and safeguards, and the exact situation depends on the provider, the request and the agreements in place.
Does this actually happen?
There are procedures and safeguards. On top of that, in 2023 the EU adopted a new adequacy decision for the EU-US Data Privacy Framework, covering transfers to certified American organisations. That decision is Implementing Decision (EU) 2023/1795. For a hospital, a law firm or a local council, it remains sensible to assess, per processing activity, which legal basis, agreements and risks apply.
What can you do?
- Choose providers that don’t fall under American law.
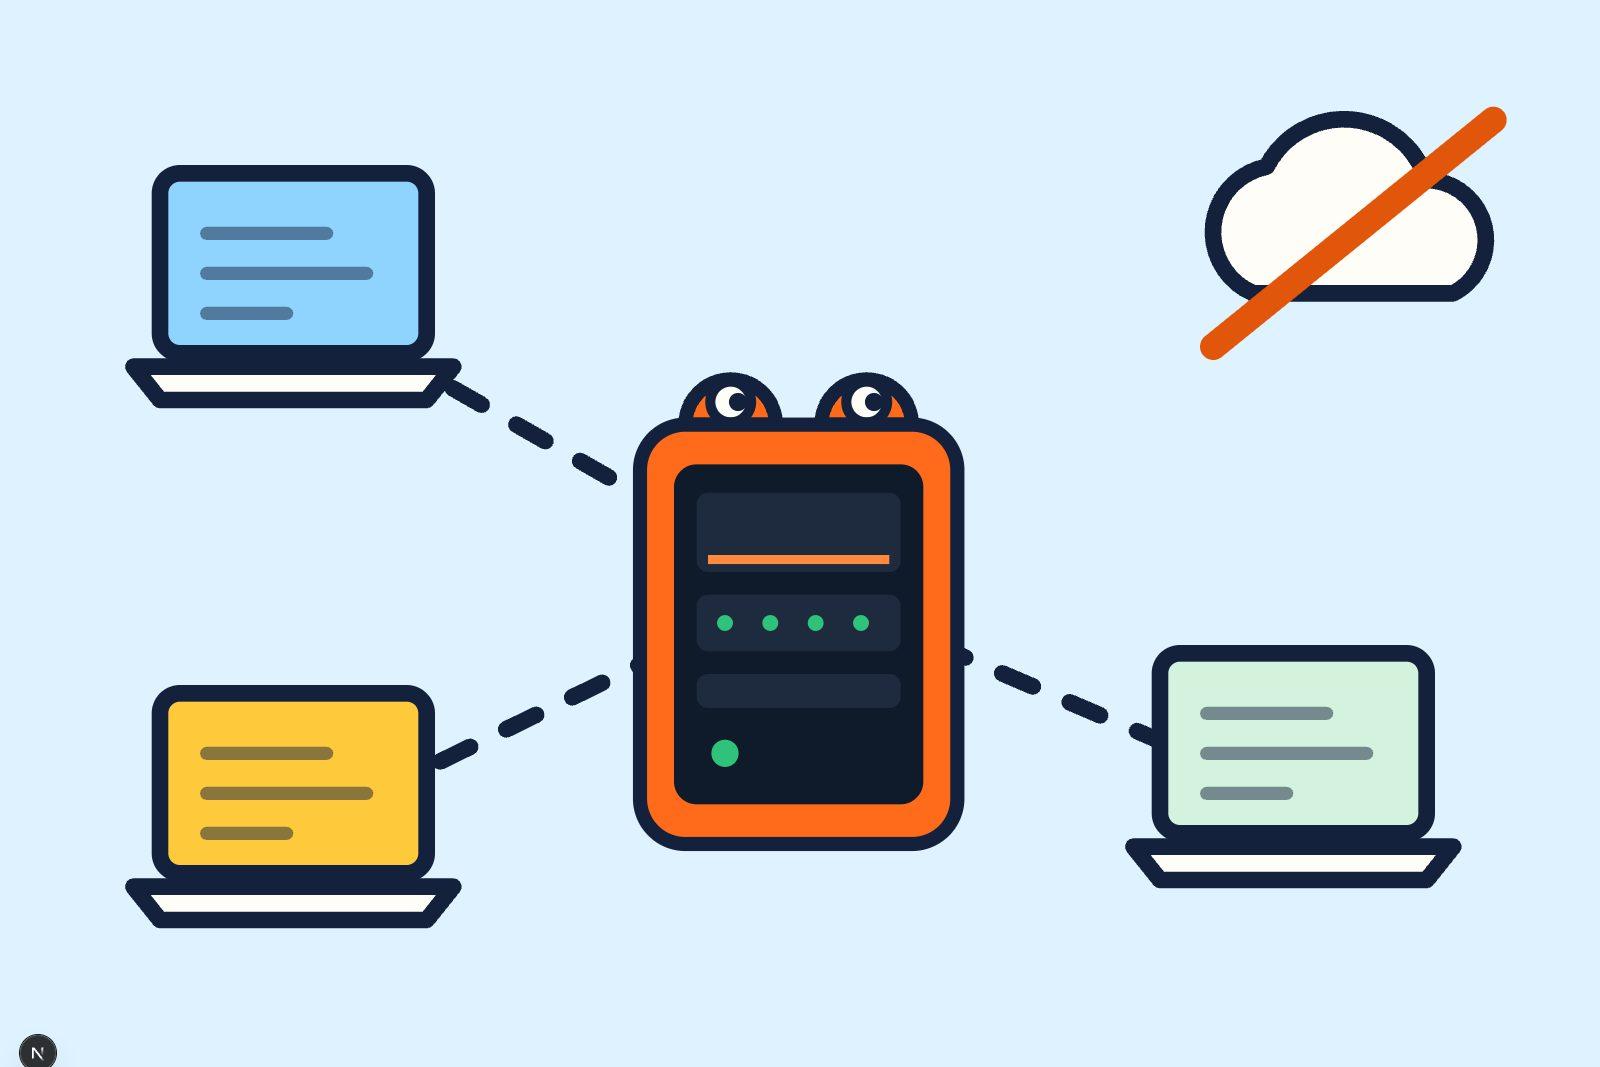
- Process sensitive documents locally when that better matches your risks and way of working. That way, questions and documents never have to go to an external AI service.
This is a simplified explanation, not legal advice.